app.virtconsole.com/kubernetes/clusters
HA control planes, node pools that mix shapes and sizes, a real cluster autoscaler, and rolling upgrades that never take the apiserver down. Provisioning finishes in 5 to 12 minutes.
Launch a cluster in minutes from a six-step wizard. Provisioning finishes in 5 to 12 minutes with a live progress overlay.
Each cluster lives in a region of your choice. Operate clusters across many regions from the same panel.
Clusters run inside one of your VPCs. Control plane nodes sit in private subnets; workers can be private or public.
An admin-managed catalogue of supported Kubernetes versions, each with vetted images and tested upgrade paths.
Single-node or 3-node HA, always fronted by a dedicated managed load balancer.
HA clusters run a 3-node etcd quorum that tolerates the loss of any one node without an apiserver outage.
Each cluster exposes both a public and a VPC-internal API endpoint. Restrict to private only if you like.
Bind a Let’s Encrypt or custom certificate to the API LB and reach kubectl at your own domain with strict TLS verification.
Download a ready-to-use kubeconfig from the cluster page, served by System DNS name rather than a bare IP.
Pin a fixed count, or set bounds and let the autoscaler respond to pod demand.
Workers scale up when pods are pending, down when nodes are underutilised. Bounds are enforced strictly so costs never run away.
Mix node shapes in one cluster: per-pool plans, labels, taints, autoscaling bounds and drain policy. A general pool beside a GPU pool.
Change a pool’s instance plan with live workers. Replacements provision first, then old nodes drain, wave by wave with zero capacity loss.
NoSchedule, PreferNoSchedule or NoExecute, pushed to every worker, applied at exactly the moment rotation reschedules pods.
Removing a worker cordons it, evicts pods within a configurable grace period, then deletes the VM. PDBs are respected.
CPU and memory donuts, pod-level utilisation and top consumers straight from the panel. No kubectl top required.
One-click upgrades for control plane and workers, wave by wave, apiserver always available.
Configure how many extra workers run in parallel: 1 means one-at-a-time with zero overhead, higher means faster.
One new CP node provisioned, one old drained, repeated until done. The apiserver stays available across all waves.
Kubernetes forbids skipping minor versions, so the dropdown only shows versions you can actually reach.
Apply a Service of type LoadBalancer and a real platform LB appears with a public IP within minutes.
Pre-installed integration that watches Services and Nodes and reconciles them against the platform.
Plan, backend protocol, Let’s Encrypt SSL, source ranges, PROXY protocol. Scaled workers appear in the LB pool within seconds.
Annotate a Service as internal and it gets a private VIP inside the VPC instead of a public IP.
Defense in depth on battle-tested upstream components. Nothing exotic.
Separate rule sets for the API LB, control plane and workers, controllable from the panel.
Set the cluster-wide default profile at create time: privileged, baseline or restricted.
eBPF kube-proxy replacement, faster than iptables, with native NetworkPolicy support. kubeadm, kubelet and containerd from pkgs.k8s.io.
Cluster PKI, autoscaler tokens and the CCM rotate 30 days before expiry. Workloads keep running.
HMAC-signed lifecycle event webhooks with per-subscription delivery history, manageable over the API.
Destructive operations like scale, upgrade and delete sit behind permissions that match your team structure.
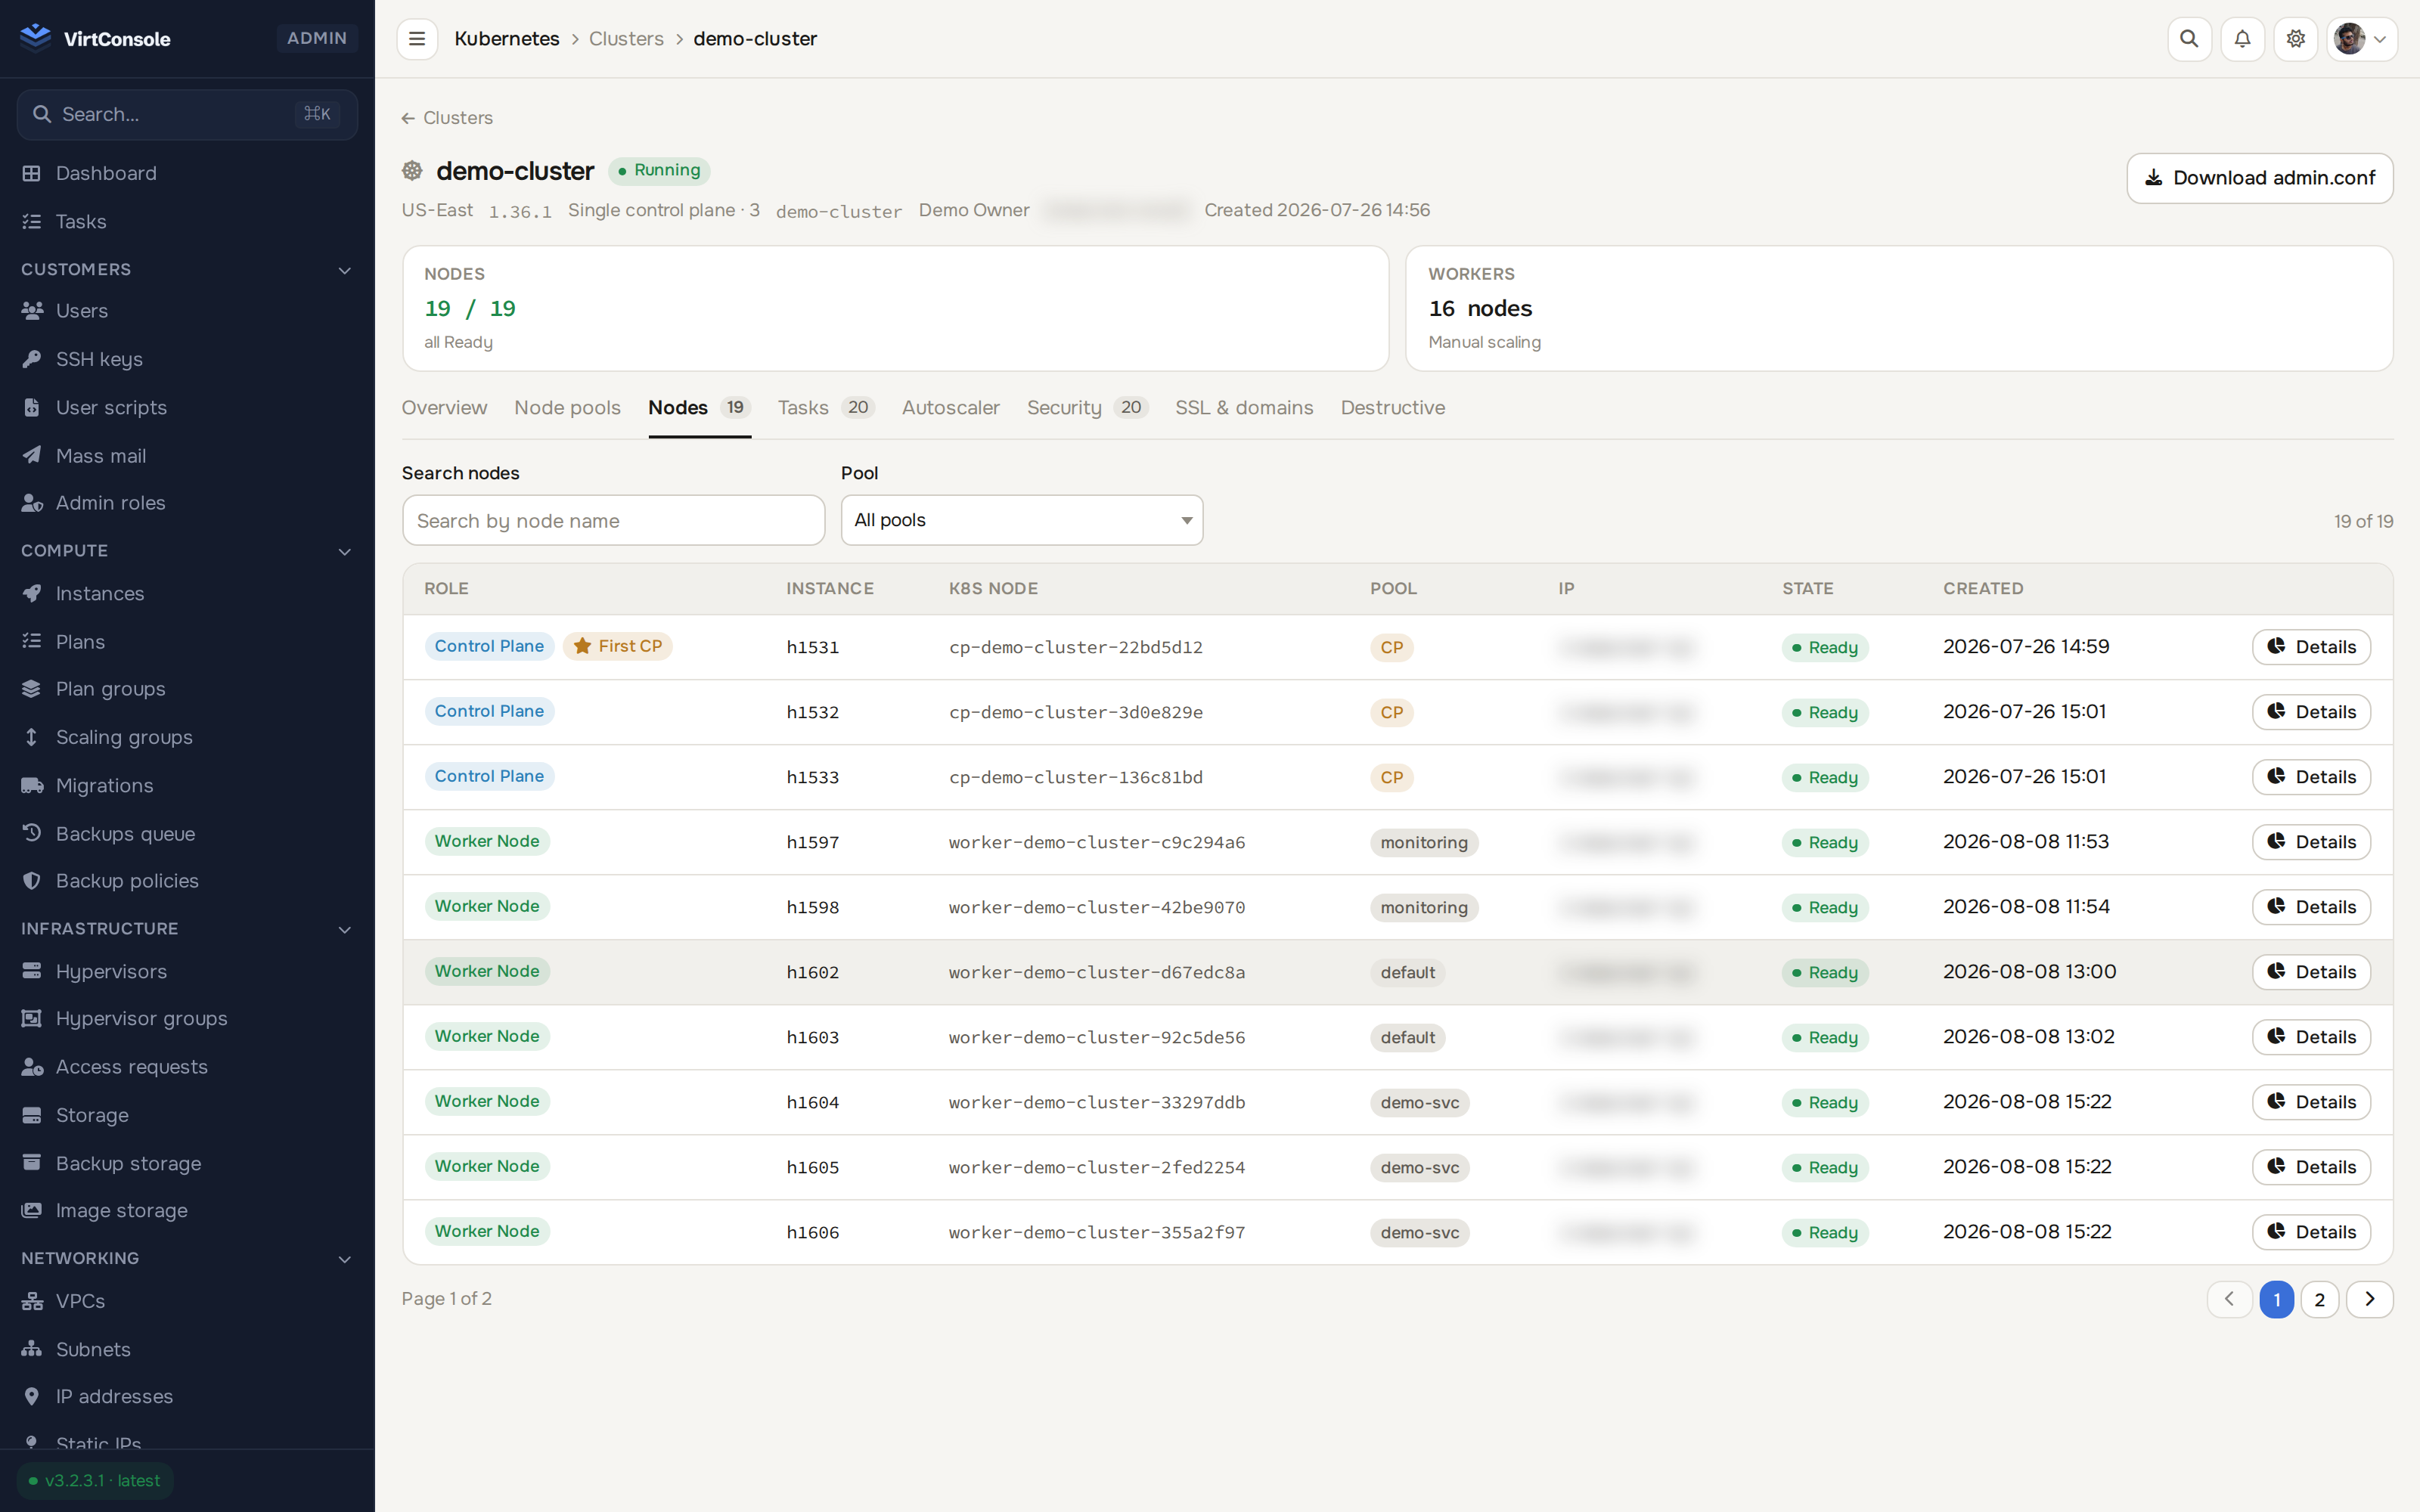
Control plane status, node pools and worker inventory in a single view, no kubectl required.
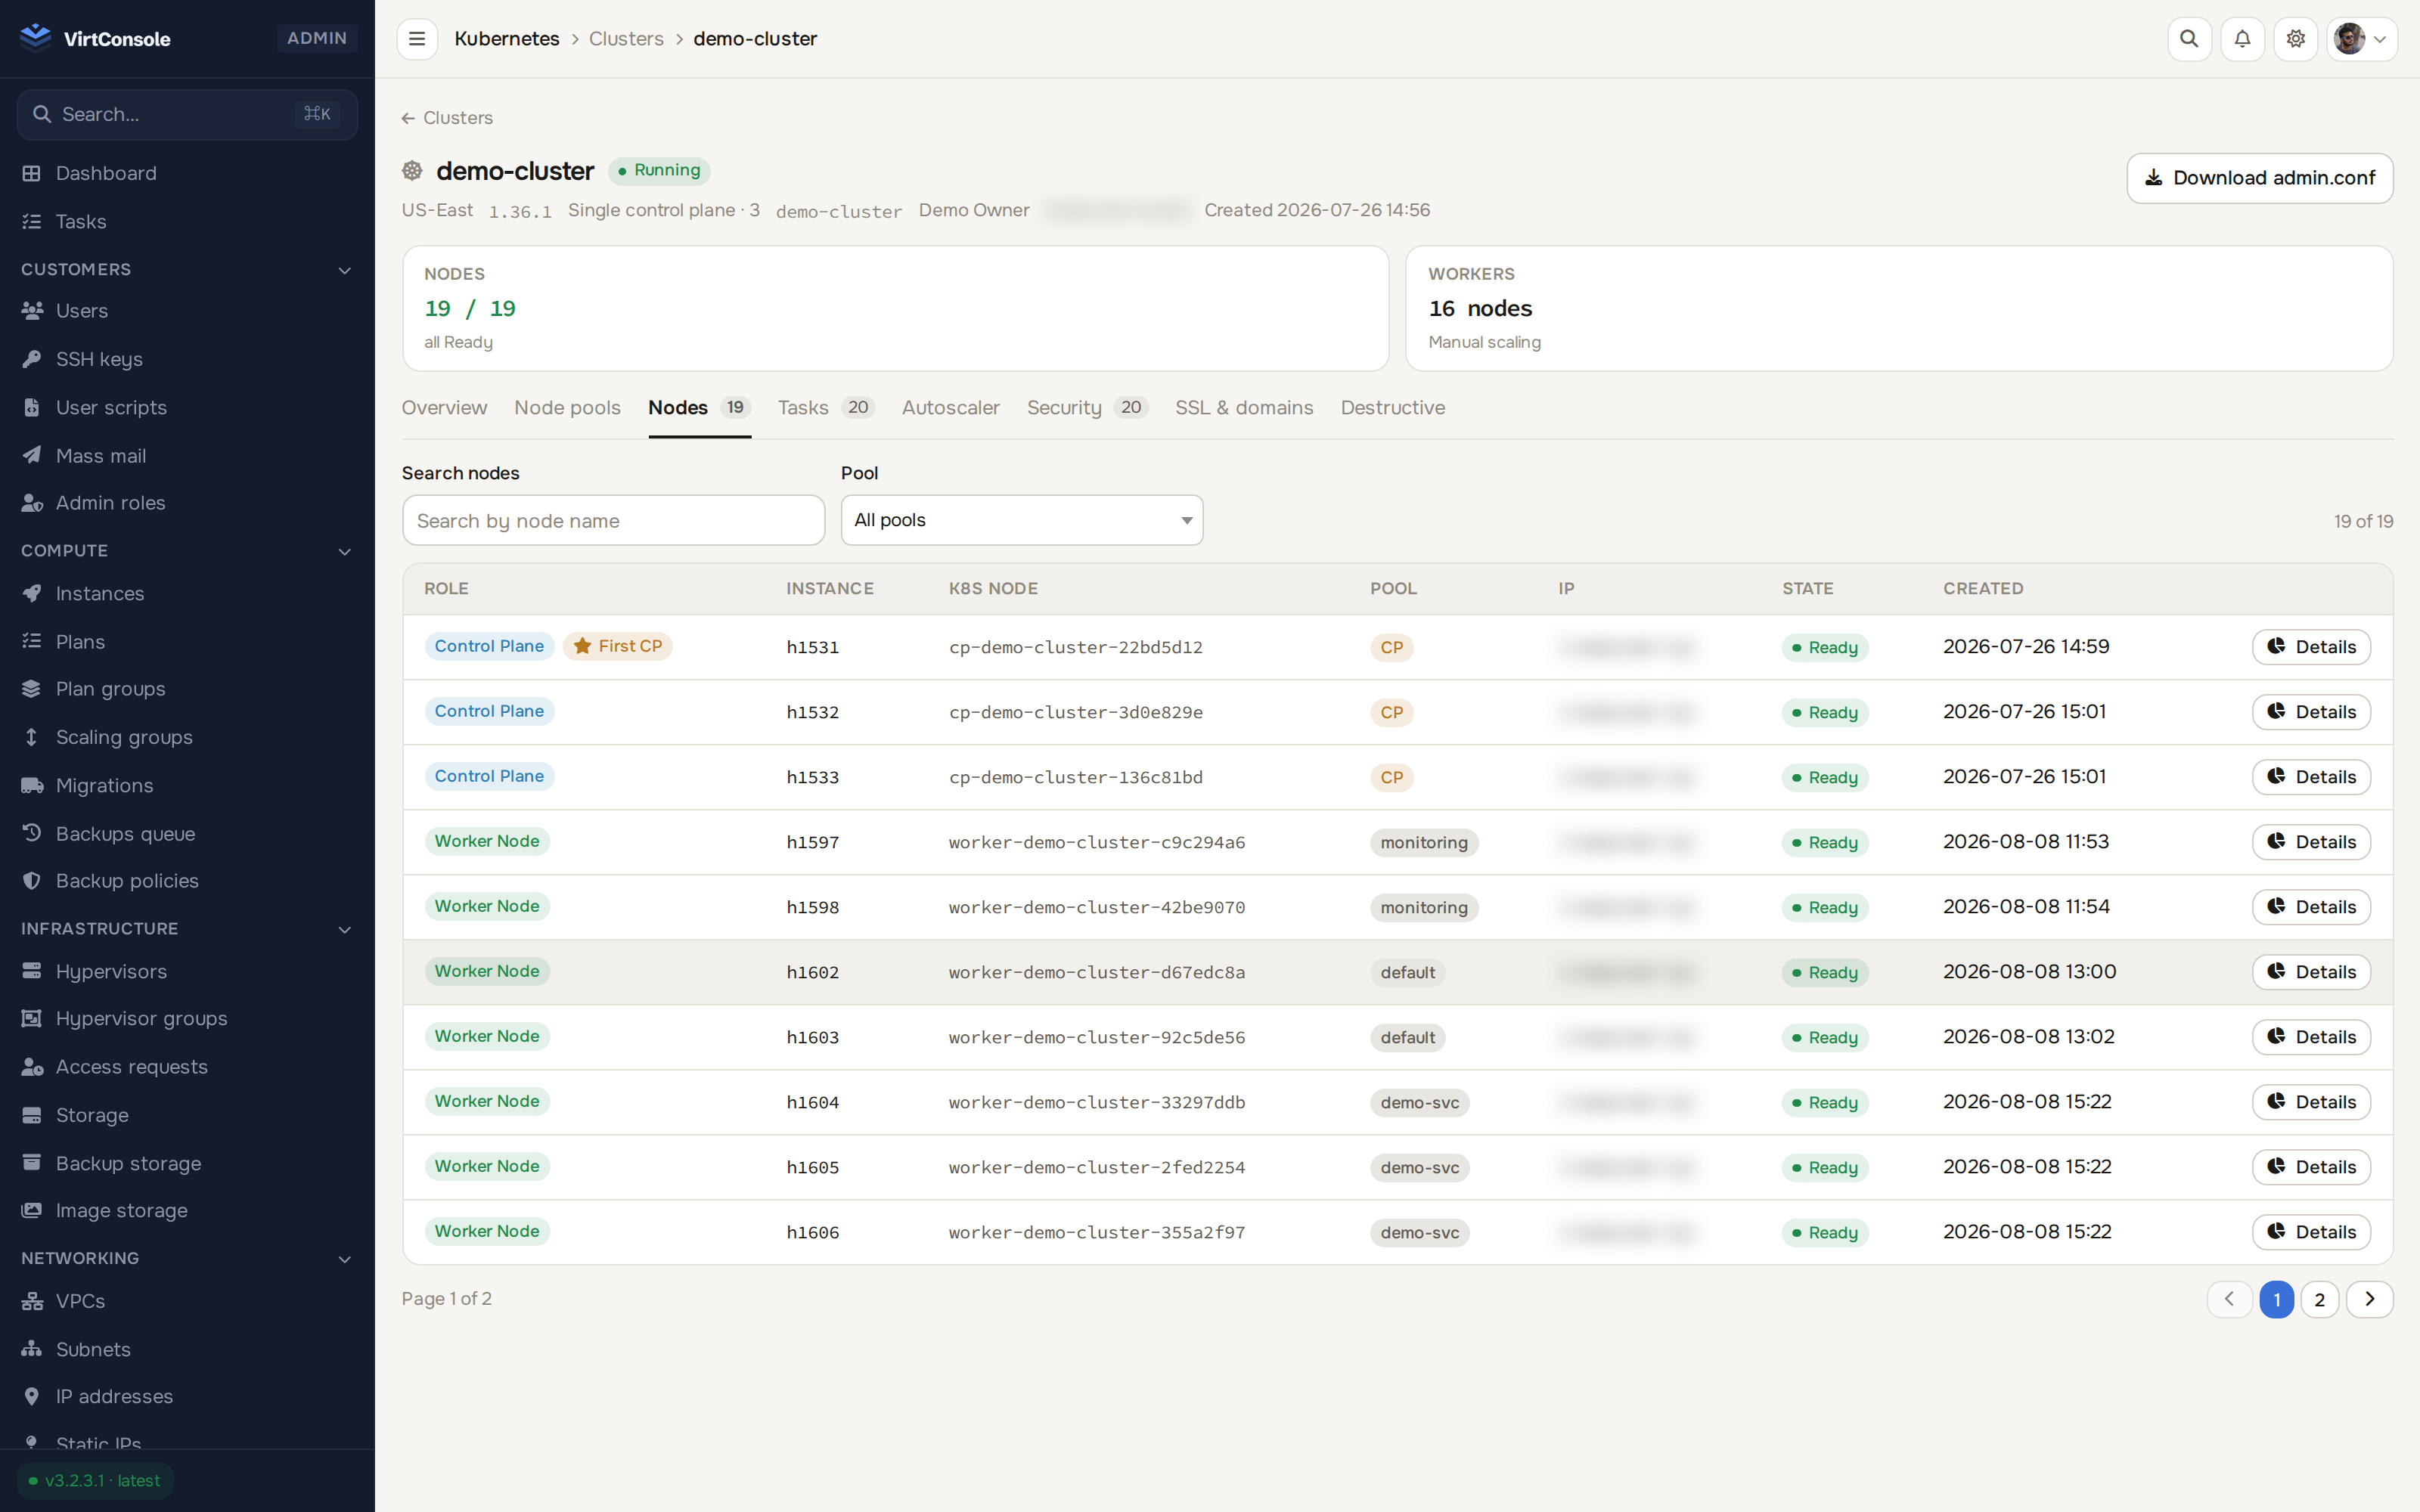
A cluster open: control plane health, pools and workers together
Free 30-day trial. Every feature included. No credit card required.
30 days, every feature, no credit card, VirtConsole installs with the trial active by default. Just run the installer on your own hardware.
Debian 11/12/13 · Ubuntu 22.04/24.04/26.04 · Rocky / Alma / CentOS Stream 9/10 · run as root.