app.virtconsole.com/settings/teams
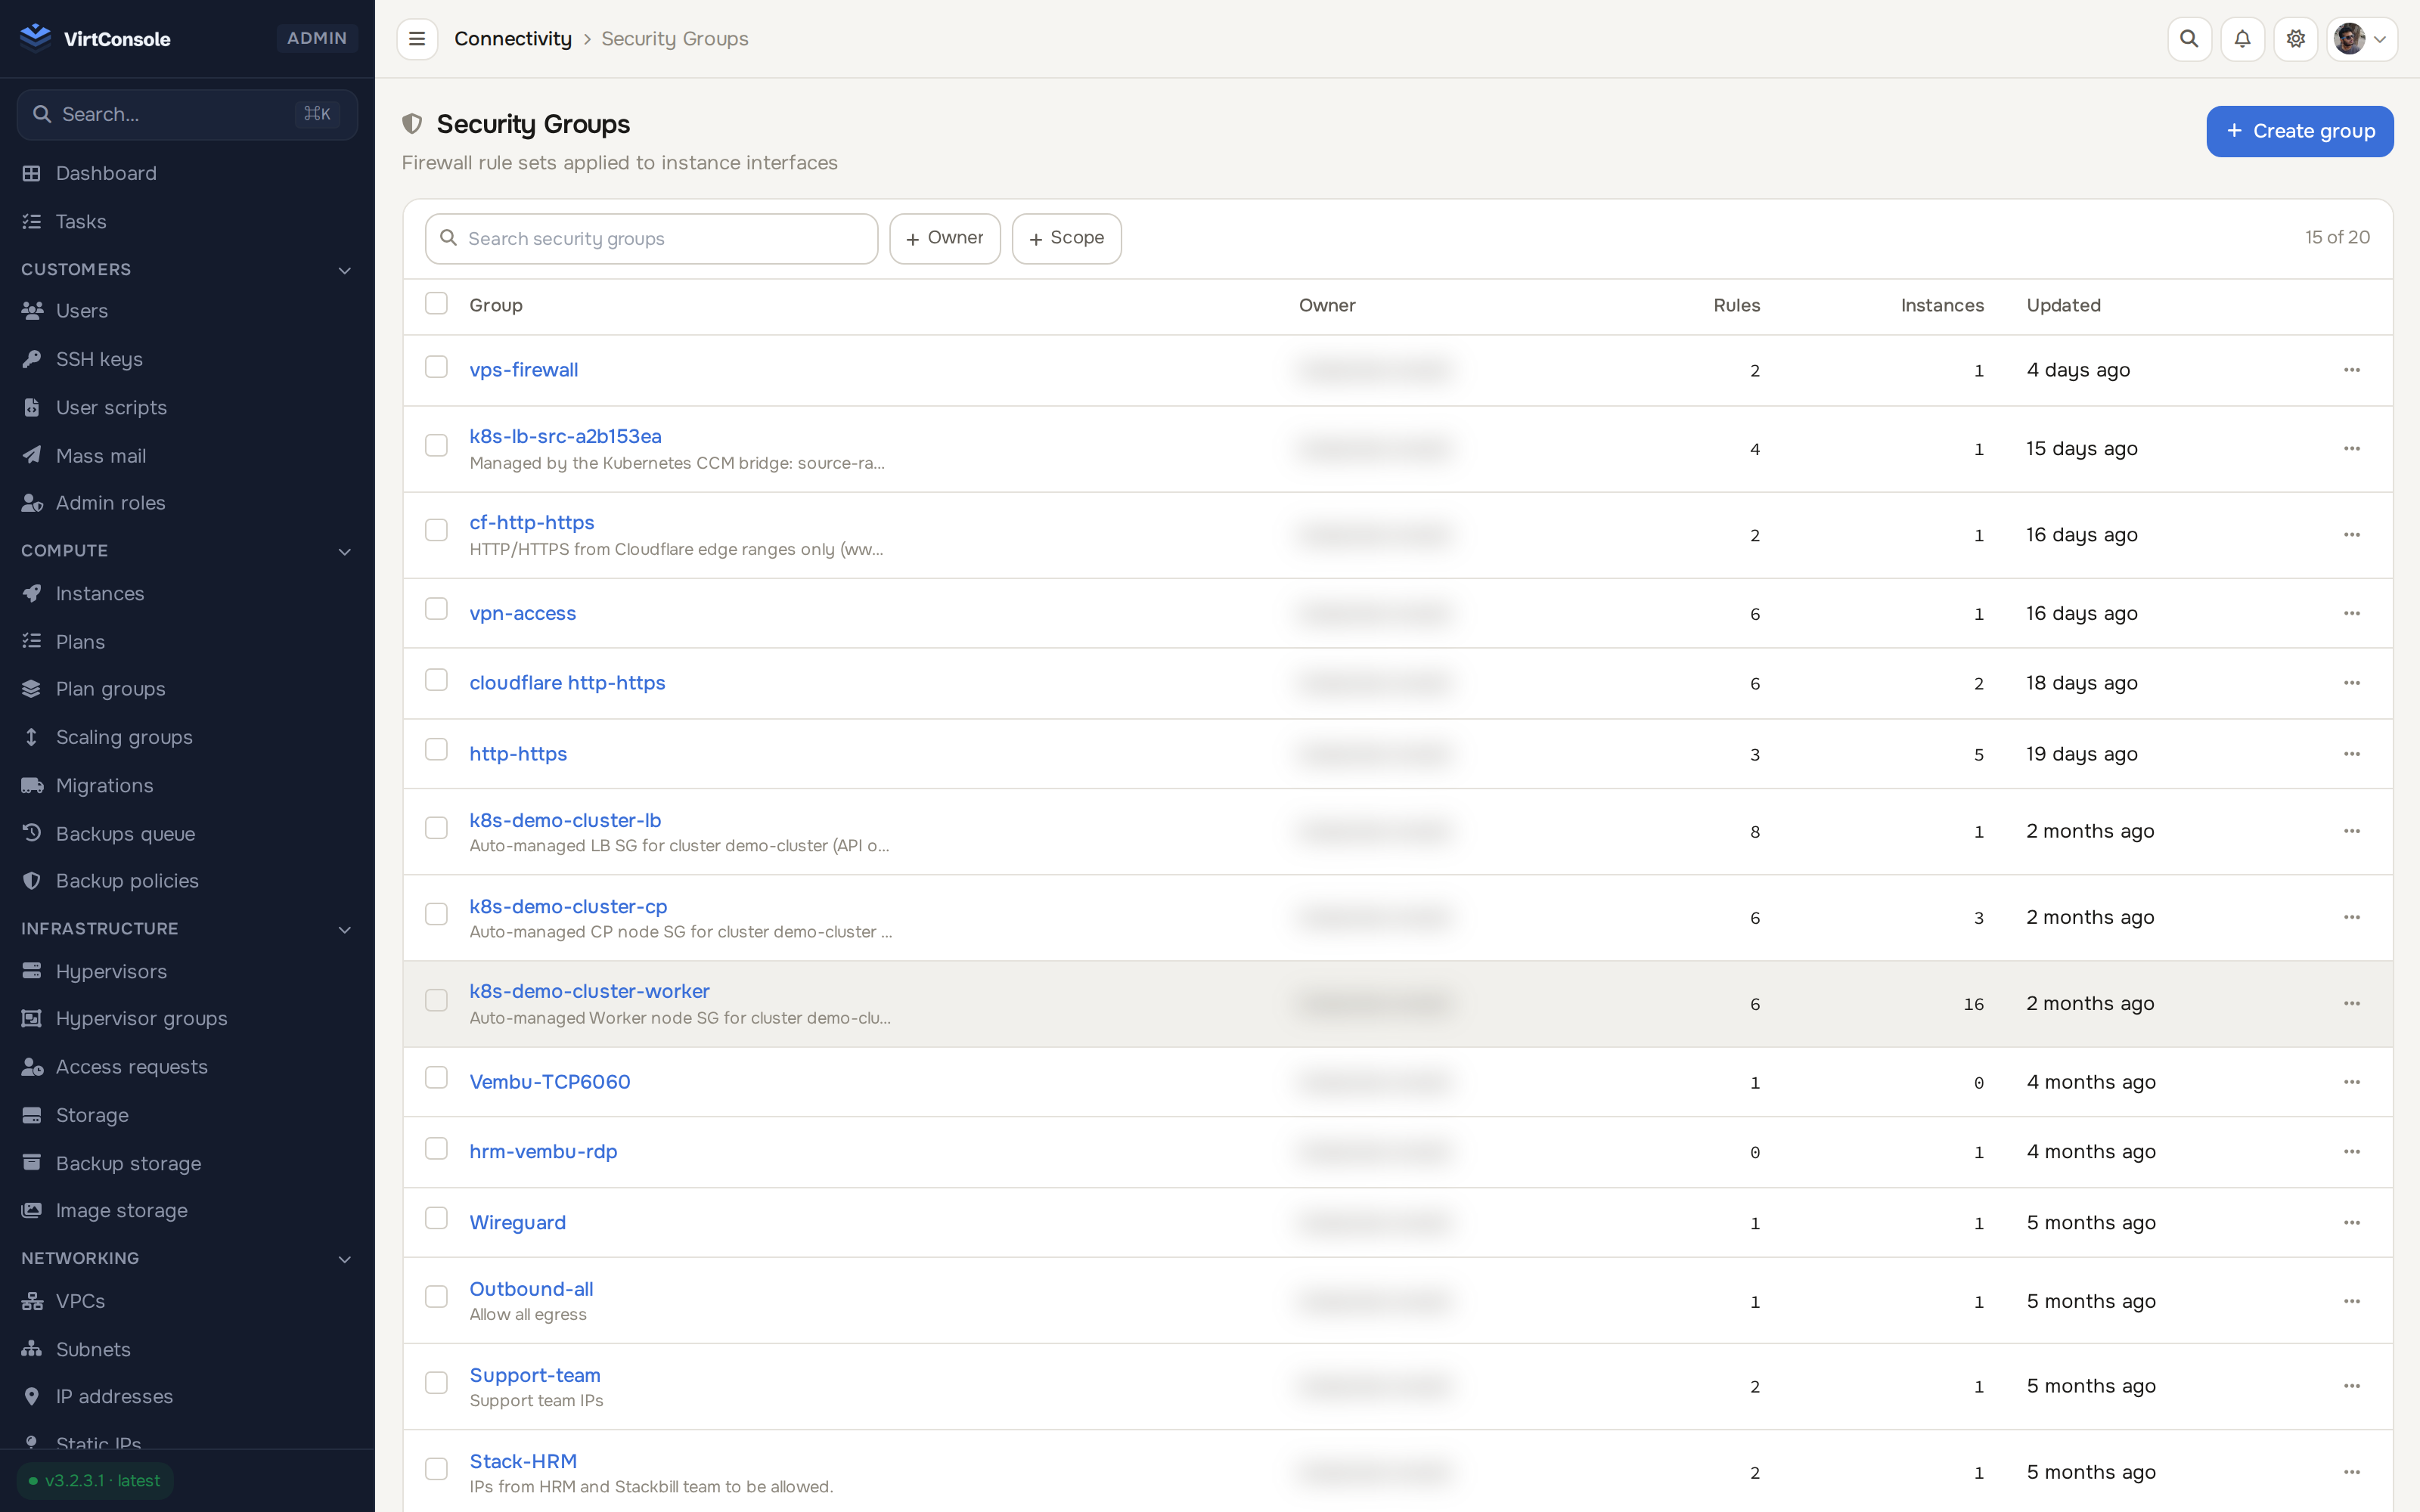
OAuth and OIDC admin SSO, team RBAC with scoped subusers, and security groups enforced identically on KVM and Proxmox.
Modern authentication for customers and staff, with conservative linking rules.
Google, Microsoft and GitHub login and registration. Auto-linking only on provider-verified emails, with known cross-tenant takeover patterns rejected.
Bind admin logins to Okta, Entra ID, Keycloak or any OIDC IdP with strict subject binding, no just-in-time provisioning, and a logged break-glass path.
Onboard customers without admin involvement: Turnstile or reCAPTCHA, signed email verification, and a post-verification top-up flow.
The right people see the right resources, and nothing else.
Multi-account teams with role-based permissions. Destructive operations sit behind separate grants.
Subuser tokens see exactly the resources their team permissions grant, across the API, metrics export and support queues.
Lock any region to selected accounts. Locked regions stay visible with a request-access flow and an admin approval queue.
Guardrails at every layer.
Per-instance accept and drop rules with IP sets and anti-spoofing filters, enforced identically on KVM and Proxmox.
On a KVM node running ConfigServer Firewall, the hypervisor agent detects it and leaves host port management to CSF instead of fighting it for the INPUT chain. Security groups, VPC NAT and the console proxies keep working alongside csf.conf.
SSH sessions, S3 keys, certificate renewal and VPC selection all bind to the owning tenant. Server-side gates on every create path.
Audit trails across the platform, with secrets encrypted at rest and in queue payloads.
The assistant gets defense in depth: streaming egress redaction, fail-closed knowledge scoping, and untrusted-data framing around tool output.
Every node carries a live checklist of the real deploy gates, with failure-specific fix hints instead of log spelunking.
Customers see clear messages; admins get the precise original error, throttled per distinct cause, and everything is logged.
Staff and customer accounts in one list, with the role-based permissions each one carries.
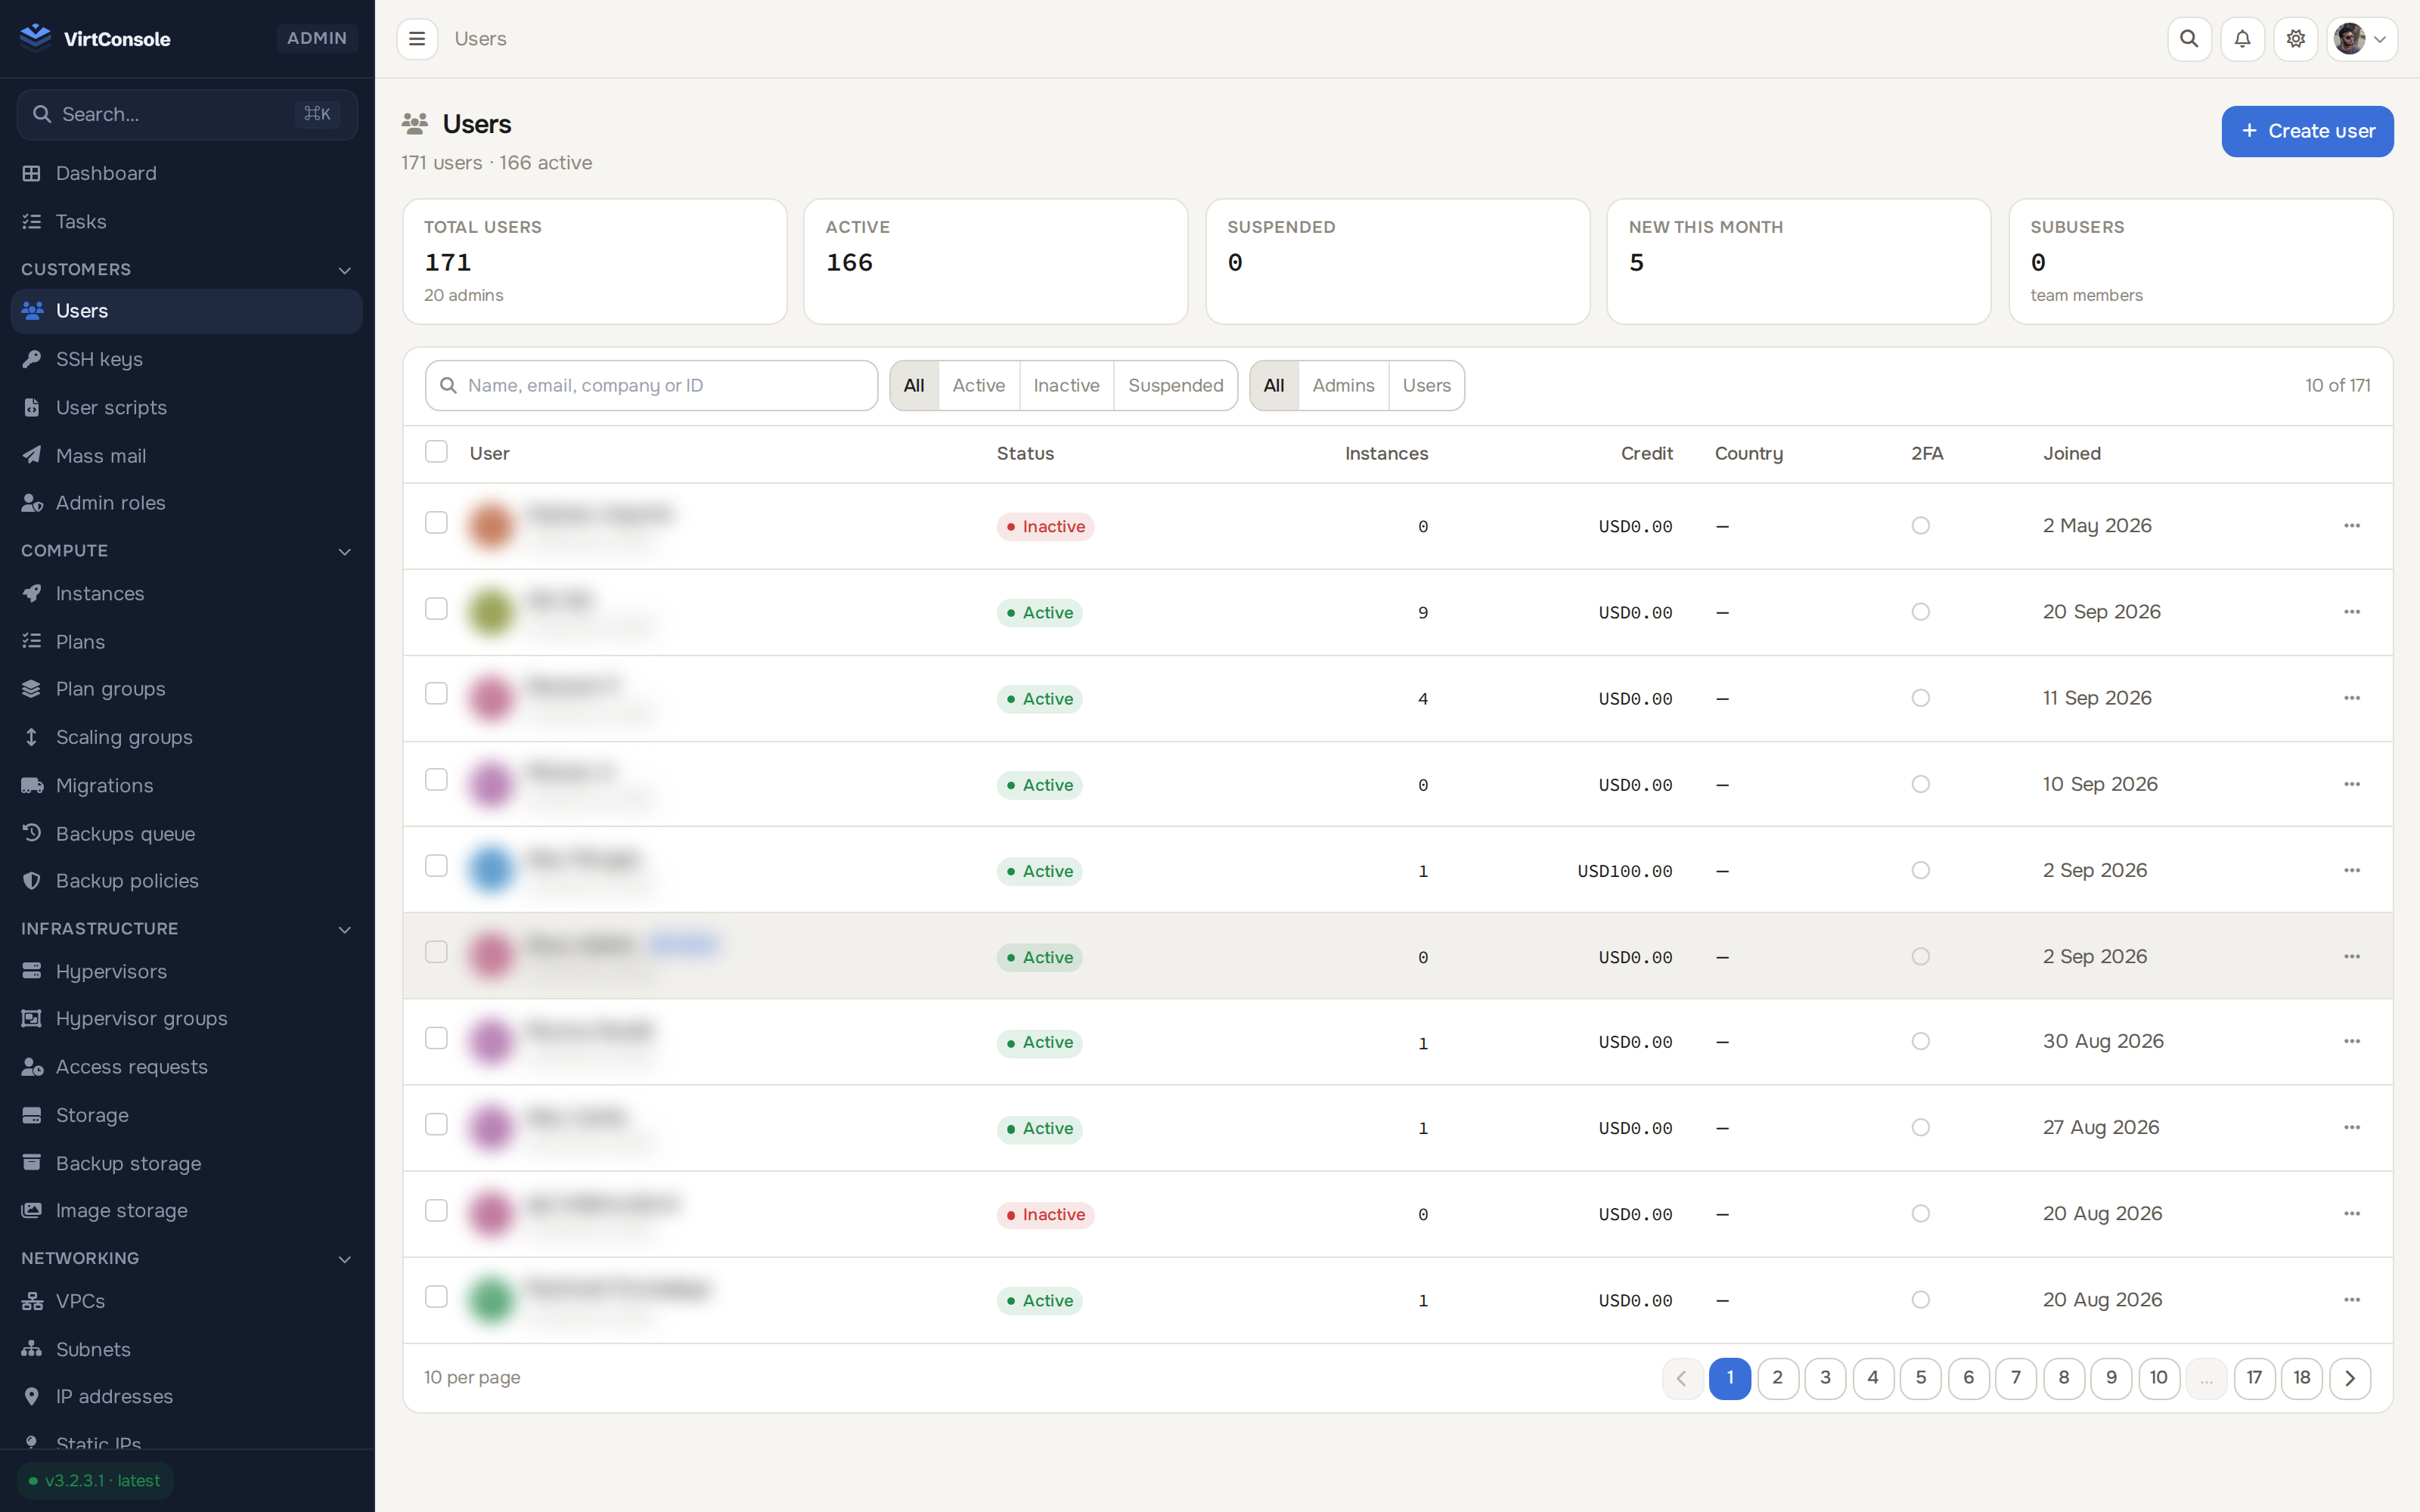
Every account, its role, and its status, searchable
Free 30-day trial. Every feature included. No credit card required.
30 days, every feature, no credit card, VirtConsole installs with the trial active by default. Just run the installer on your own hardware.
Debian 11/12/13 · Ubuntu 22.04/24.04/26.04 · Rocky / Alma / CentOS Stream 9/10 · run as root.